
Escalating Signalling Attacks
SS7 and Diameter attacks involving location tracking, call interception and fraud injection are growing in sophistication and volume
We bring AI-driven security operations, signalling protection, voice security, fraud and revenue assurance, spam control and content security together to protect operator networks, revenue and subscribers through one connected security environment.
Industry Challenges
Threats increasingly cut across signalling, voice, data and subscriber environments. When security systems operate independently, teams have limited cross-domain visibility, fragmented threat intelligence and slower response to attacks that move across multiple network layers.
SS7 and Diameter attacks involving location tracking, call interception and fraud injection are growing in sophistication and volume
SIM box fraud, bypass schemes, Wangiri and unauthorised tethering create direct revenue exposure, while detection and investigation often happen after the event.
Security teams manage thousands of daily alerts across firewalls, fraud platforms and DPI systems, making critical threats harder to prioritise and correlate.
Voice and SMS spam erode subscriber trust and increase regulatory scrutiny, while evolving patterns challenge static signature-based filtering.
Operators have trusted network assets and established customer relationships but need the right platform to package and deliver cybersecurity services commercially.
Solution Overview
We create a more coordinated approach to telecom security, where threats can be identified across domains, intelligence can inform response and risks to the network, subscribers and revenue can be addressed as part of the same security posture.
Signalling, voice, data, fraud and content-security intelligence come together to provide a broader view of threats across the telecom environment.
AI-driven correlation and prioritisation help security teams identify critical incidents faster and coordinate appropriate response across connected security controls.
Fraud detection and revenue assurance connect security intelligence with commercial exposure, helping identify activity that threatens both network integrity and operator revenue.
Security-as-a-Service capabilities create opportunities to package selected cybersecurity services for enterprise and consumer customers as part of the broader operator security proposition.
Solution Capabilities
Each security capability protects a distinct part of the telecom environment, while shared intelligence and AI-driven operations help connect detection and response across the suite.
Agentic AI brings alerts from multiple security systems together, correlates threats across domains, prioritises incidents and executes approved response actions such as blocking or isolation within defined policy guardrails.
Signalling firewalls provide real-time threat detection, intelligent filtering and automated response across SS7 and Diameter environments.
Real-time call analysis detects Wangiri, robocalls, CLI spoofing and international revenue-share fraud using AI pattern recognition and DPI.
Machine-learning models and DPI-powered traffic analysis identify SIM box fraud, bypass schemes, unauthorised tethering and revenue anomalies, helping operators detect and address revenue leakage earlier.
Multi-channel detection and blocking identify evolving spam patterns across voice, SMS and data beyond static rule-based filtering.
An operator-branded cybersecurity marketplace enables curated services such as endpoint protection, DNS security, VPN and threat intelligence to be offered to enterprise and consumer customers.
Threat intelligence is shared across security components, allowing activity identified in one domain to strengthen detection and response across others.
IWF Firewall provides carrier-grade content filtering to support regulatory, child-safety and enterprise content policies.
Business Impact
Real-time AI-driven fraud detection and automated blocking help identify and stop revenue-draining schemes as they occur rather than weeks later through reconciliation.
AI-SOC automates alert prioritisation, threat correlation and first-response actions across security domains, reducing response times from hours to minutes.
Signalling and content-security capabilities support GSMA IR.82/FS.11 and applicable regulatory requirements, helping operators strengthen compliance across the telecom environment.
Security-as-a-Service enables operators to package curated cybersecurity capabilities for enterprise and consumer segments, extending security into a new commercial proposition.
Connected visibility across signalling, voice, data and content security reduces the blind spots created by isolated defence systems.
Machine-learning models continuously learn from new attack patterns, strengthening threat detection as threats evolve rather than depending solely on static rules and manual updates.
Use Cases
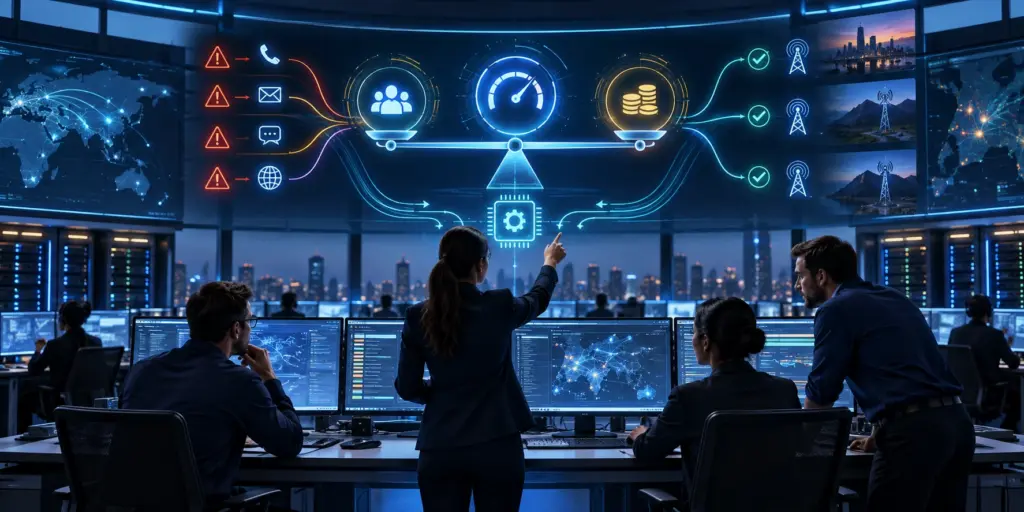
A national operator consolidated three separate security monitoring teams covering signalling, fraud and content under AI-SOC. The platform…
A national operator consolidated three separate security monitoring teams covering signalling, fraud and content under AI-SOC. The platform ingested 500K+ daily alerts, correlated them into approximately 150 prioritised incidents and automatically resolved 45% within defined policy guardrails. Security resources were redeployed from routine monitoring to threat hunting.
DPI and CDR analytics detected SIM box fraud through unusual international-to-local call ratios, SIM rotation patterns and geographic…
DPI and CDR analytics detected SIM box fraud through unusual international-to-local call ratios, SIM rotation patterns and geographic anomalies. Automated blocking reduced bypass-fraud losses by $4M annually within the first six months.
An operator deployed the Security-as-a-Service marketplace with DNS security, endpoint protection and managed threat intelligence for enterprise customers.…
An operator deployed the Security-as-a-Service marketplace with DNS security, endpoint protection and managed threat intelligence for enterprise customers. Within 12 months, 8% of enterprise subscribers adopted at least one security service, generating $2M in incremental annual revenue.
AI-SOC detected a coordinated SS7 location-tracking attack targeting VIP subscribers and automatically applied enhanced signalling firewall rules within…
AI-SOC detected a coordinated SS7 location-tracking attack targeting VIP subscribers and automatically applied enhanced signalling firewall rules within 30 seconds, blocking the attack before subscriber location data was exposed.