
Encrypted Traffic Limits Traditional Content Visibility
Growing encryption makes it harder for conventional filtering approaches to accurately identify domains, applications, and content categories.
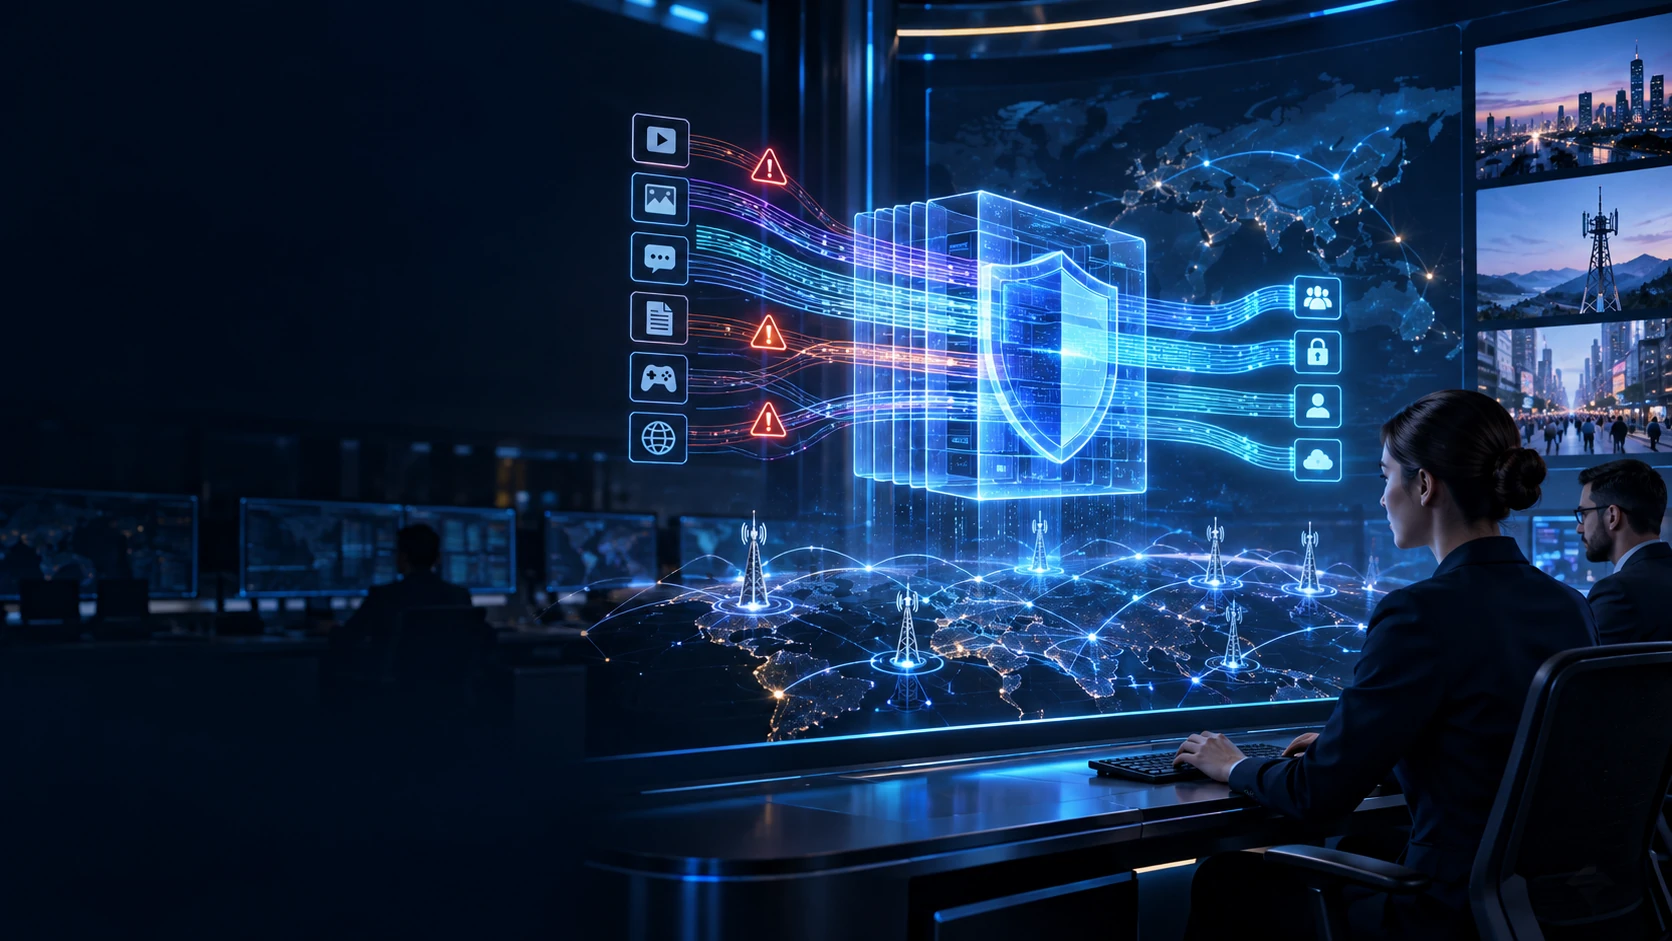
We combine deep packet inspection with intelligent content classification to enforce real-time access policies, strengthen subscriber protection, and support regulatory compliance across operator networks.
Challenges
Growing encryption makes it harder for conventional filtering approaches to accurately identify domains, applications, and content categories.
Operators need reliable content controls to meet regulatory mandates while minimizing unnecessary disruption to legitimate digital services.
New domains, URLs, applications, and content patterns emerge rapidly, reducing the effectiveness of static blocklists and predefined categories.
Child safety, enterprise policies, and individual subscriber preferences require flexible content controls that can be applied at scale.
Product Overview
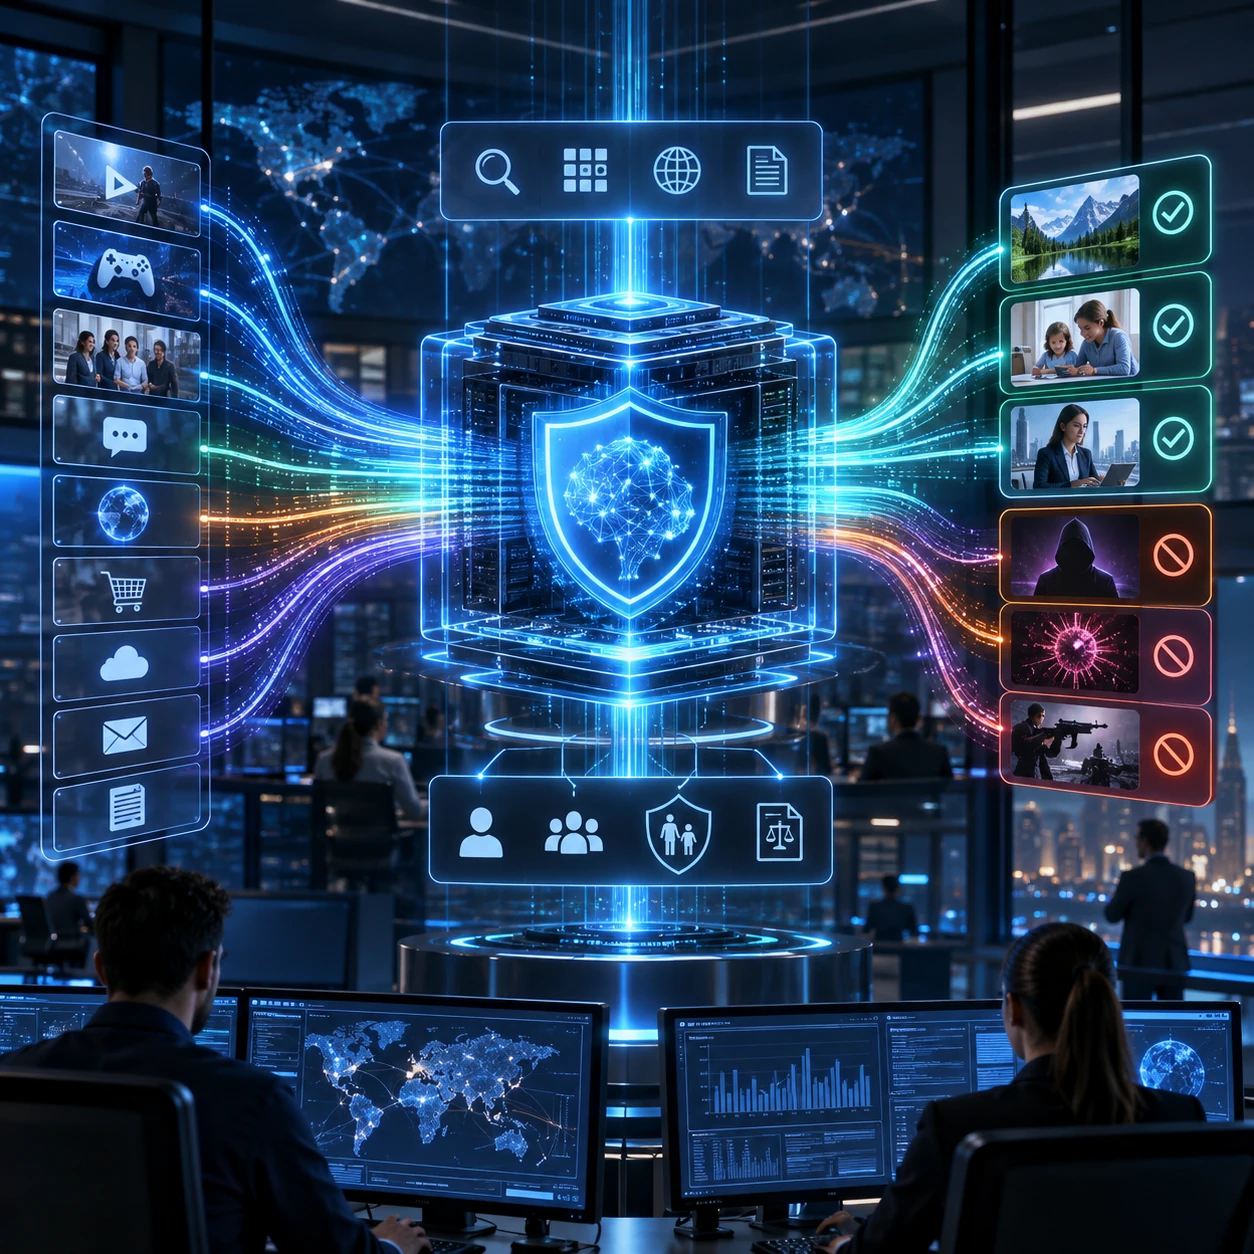
Our IWF Firewall provides carrier-grade content filtering and policy enforcement using Deep Packet Inspection (DPI). It performs real-time URL filtering, domain blocking, SNI analysis, and payload-level content classification to support child safety, prohibited-content blocking, regulatory requirements, and enterprise content policies.
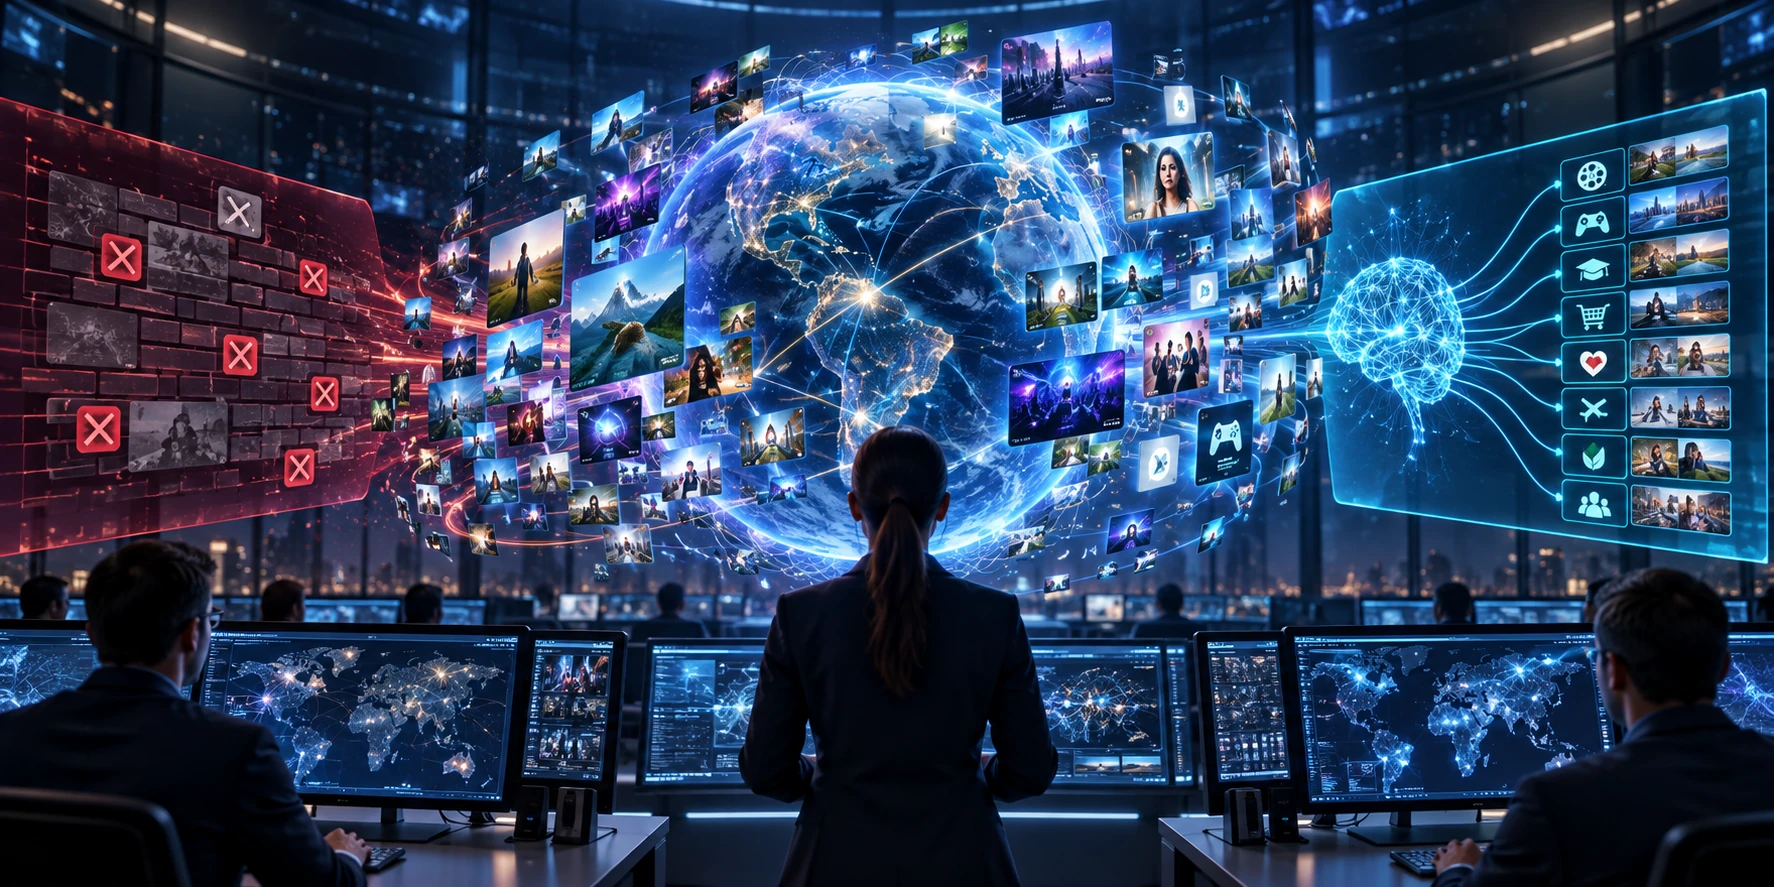
ML-enhanced categorization improves classification accuracy for encrypted traffic, new domains, and emerging threats, while AI-driven parental controls enable configurable subscriber protection and self-service policy management.
The Outcomes Are Clear
Capabilities

Inspect application-layer traffic and supported payload information to identify content, services, and traffic characteristics requiring policy action.

Apply configurable access policies to URLs and domains based on regulatory, safety, enterprise, or operator requirements.

Analyze Server Name Indication (SNI) and associated traffic characteristics to strengthen visibility and classification of encrypted connections.

Inspect supported application-layer payload information to classify content and enforce granular protection policies in real time.

Improve classification accuracy for encrypted traffic, new domains, emerging threats, and evolving content patterns using machine learning.

Enable intelligent parental control capabilities with configurable protection policies designed to support safer digital experiences.

Allow subscribers to manage eligible content access and protection preferences through supported self-service capabilities.

Manage regulatory, child-safety, enterprise, and subscriber-specific content policies through a unified operational environment.
Process
DPI analyzes application-layer traffic, URLs, domains, SNI information, and supported payload characteristics in real time.
ML-enhanced categorization identifies content types, new domains, encrypted traffic characteristics, and emerging threat patterns.
Traffic is assessed against regulatory, operator, enterprise, child-safety, or subscriber-specific access policies.
The platform permits, restricts, or blocks content according to the applicable policy and classification.
AI/ML-enhanced classification and configurable policies evolve with changing content patterns, emerging threats, and subscriber protection requirements.
Results
Apply consistent content controls across operator networks to support applicable regulatory mandates.
Combine DPI and ML to improve identification of encrypted traffic, new domains, and evolving content.
Provide intelligent content controls that support child safety and safer access to digital services.
Apply differentiated policies according to regulatory requirements, subscriber profiles, enterprise needs, and service configurations.
Enable self-service capabilities that allow subscribers to manage eligible content and protection preferences.
Extend content filtering into intelligent subscriber protection services that strengthen the operator's digital proposition.