
Signaling Networks Remain a High-Value Attack Surface
Attackers exploit SS7 and Diameter vulnerabilities to track subscribers, compromise privacy, manipulate services, and enable sophisticated telecom fraud.
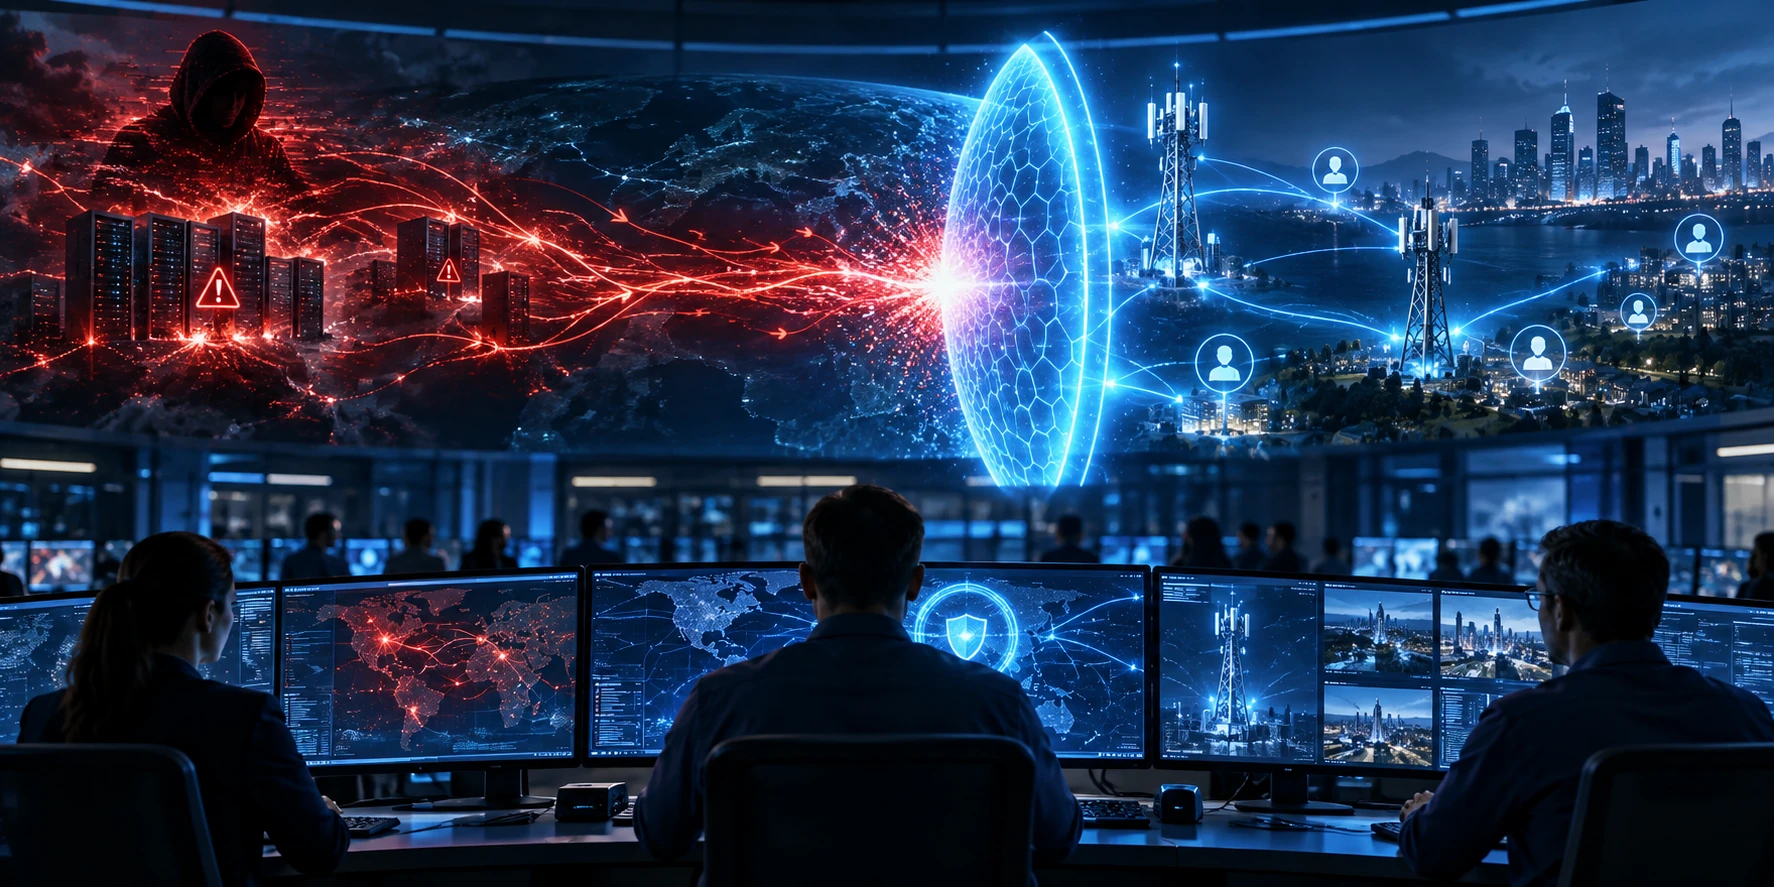
We protect SS7 and Diameter signaling environments with multi-layer security, AI/ML-powered threat detection, and real-time response controls that identify and stop known, zero-day, and advanced signaling attacks.
Challenges
Attackers exploit SS7 and Diameter vulnerabilities to track subscribers, compromise privacy, manipulate services, and enable sophisticated telecom fraud.
Known attack patterns can be filtered through predefined rules, but zero-day and advanced threats require adaptive behavioral intelligence.
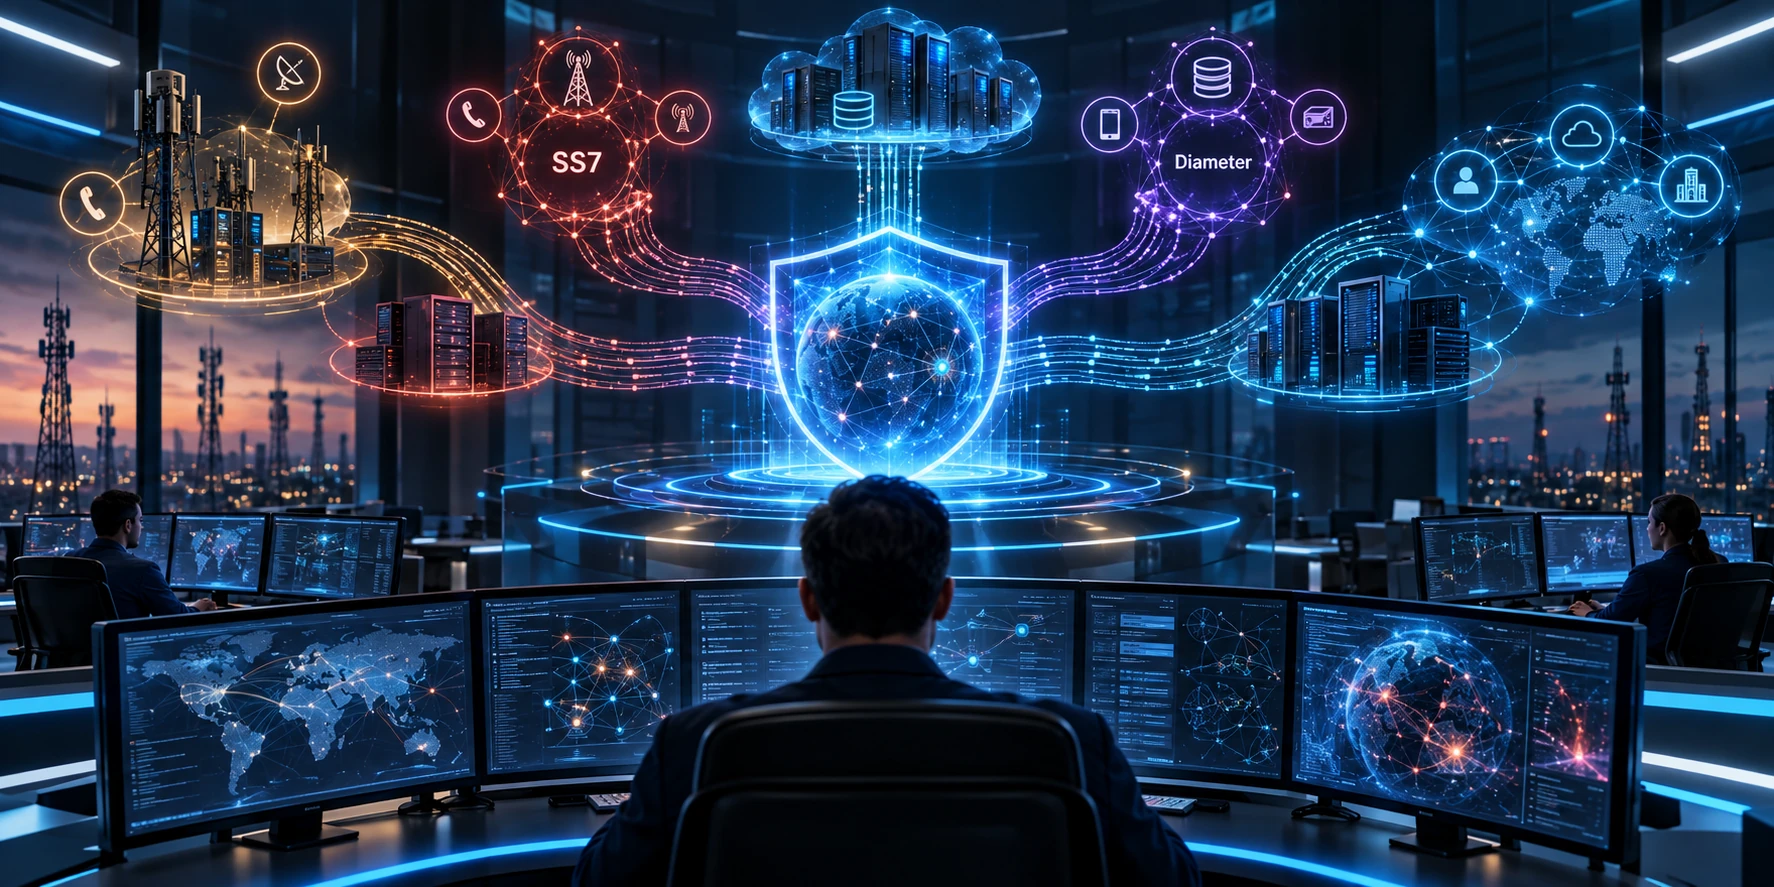
Protecting SS7, Diameter, and interconnected signaling domains requires consistent security controls and threat visibility across multiple interfaces.
Security teams need to detect, classify, and contain malicious signaling activity in real time before attacks escalate.
Product Overview
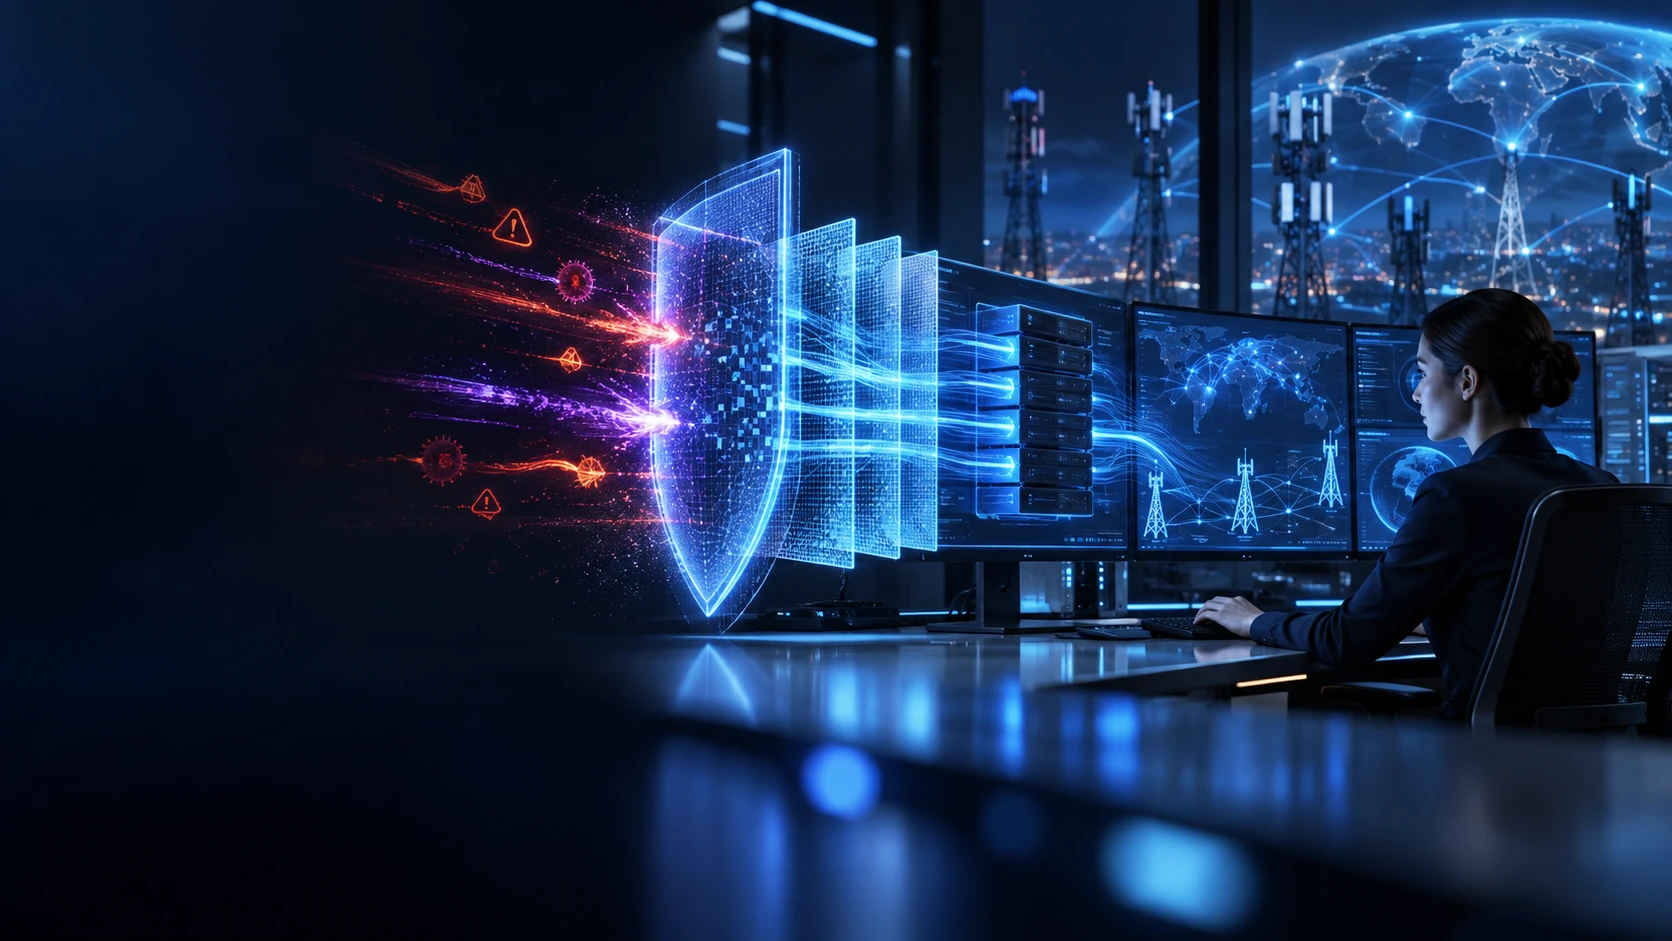
Our Signaling Firewall protects SS7 including MAP, CAP, and INAP and Diameter signaling across network interfaces. It combines GSMA FS.11 and FS.19-compliant filtering with AI/ML-powered behavioral analysis to detect known attacks, zero-day signaling threats, advanced persistent threats, and anomalous patterns that static rules can miss.
Real-time AI scoring classifies threats by severity and triggers automated block, alert, or throttle responses, while DPI correlation connects signaling-layer threats with user-plane traffic anomalies for comprehensive attack visibility.
The Outcomes Are Clear
Capabilities

Protect SS7—including MAP, CAP, and INAP—and Diameter signaling across network interfaces through centralized security controls.

Apply rule-based filtering compliant with GSMA FS.11 and FS.19 to detect and control established signaling attack scenarios.

Use ML-powered behavioral intelligence to identify zero-day signaling attacks, advanced persistent threats, and anomalous patterns that static rules can miss.

Classify suspicious signaling activity by severity using behavioral patterns and network context to support immediate security decisions.

Trigger configurable block, alert, and throttle actions in real time based on threat classification and security policies.
Correlate signaling-layer threats with user-plane traffic anomalies to provide comprehensive cross-layer attack visibility.

Continuously improve detection using community threat intelligence and adaptive ML models that learn from global attack patterns.

Provide unified dashboards for real-time threat monitoring, attack analysis, policy management, and security reporting.
Process
We continuously monitor SS7 and Diameter signaling activity across protected network interfaces.
Known attack patterns are evaluated against rule-based FS.11 and FS.19 security policies.
Adaptive ML models analyze signaling behavior to identify zero-day attacks, advanced persistent threats, and anomalous activity beyond predefined rules.
AI classifies threat severity while DPI intelligence correlates suspicious signaling events with related user-plane traffic anomalies.
Configured policies automatically block, throttle, or alert on malicious activity while confirmed threat intelligence strengthens adaptive detection models.
Results
Protect critical SS7 and Diameter infrastructure against known, zero-day, and advanced signaling threats.
Identify malicious behavioral patterns that conventional rules and signatures may not recognize.
Automate threat scoring and policy-driven responses to contain malicious activity before it escalates.
Reduce exposure to signaling attacks that can compromise subscriber location, privacy, communications, or service access.
Correlate signaling and user-plane intelligence to strengthen threat investigation and security response.
Continuously strengthen protection using community threat intelligence and ML models that learn from evolving global attack patterns.